
Tag: Cyber Security
What Microsoft’s SMS and Voice Retirement Means for Your Organization
The deadline for Entra ID authentication changes is approaching and will affect many organizations. Passkeys became the default option for eligible users in September 2026, and Microsoft-provided text and phone-call verification is scheduled to end in 2027. If businesses are still relying on SMS or voice for multifactor authentication (MFA), it is now time to… Read more
FortiBleed: From Credential Exposure to a Secure FortiGate State
FortiGate firewalls provide crucial security at the edge of an organization’s network. These firewalls protect internet-facing services, terminate VPN connections, enforce security policies, and provide the path into the internal network in many environments. When you are warned about potentially compromised FortiGate credentials across over 80,000+ verified devices across almost 200 countries, you should heed… Read more
Vishing and MFA Phishing Attacks
1. Executive Summary Threat actors are targeting banking clients through coordinated social engineering campaigns that leverage sophisticated voice phishing (vishing), bank impersonation, caller ID spoofing, credential-harvesting websites, and MFA social engineering. These attacks are conducted in real time, allowing threat actors to capture victims’ banking credentials and authentication codes and immediately use them to access… Read more
Agentic Artificial Intelligence
When most people think of Artificial Intelligence (AI), they think of the widespread, commercial, chatbot-like platforms. You type something, and it types something back; the user initiates actions. An “agent” is different. It can browse the web, write and run code, call other software, and chain multiple steps together to complete a task without a… Read more
Why Firewalls and Edge Gateways are the New Primary Target
For a long time, the unwritten rule of initial access was simple- trick a human. Phishing and social engineering were the easiest ways into a network because people are notoriously easy to manipulate. While those vectors haven’t gone anywhere, the threat landscape has shifted drastically over the past year. Sophisticated threat actors are completely bypassing… Read more
How Threat Actors Are Abusing Microsoft Entra ID Self-Service Password Reset (SSPR) to Compromise Cloud Environments
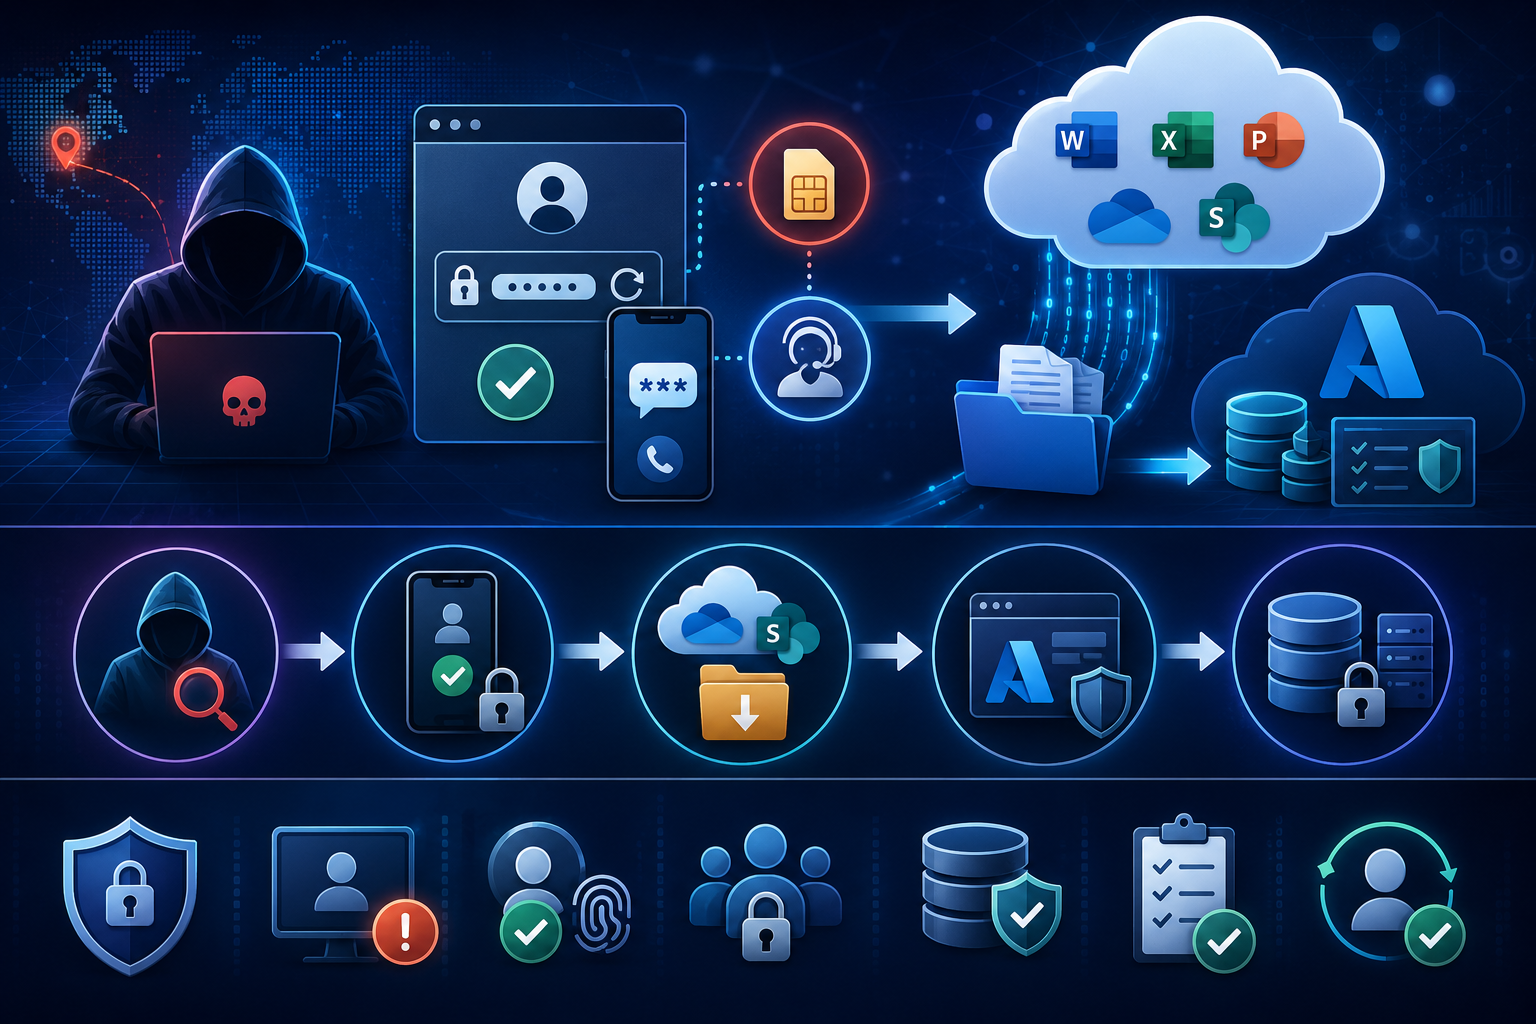
Threat actors are increasingly leveraging Microsoft Entra ID’s Self-Service Password Reset (SSPR) feature to conduct highly targeted, identity-driven attacks. Advanced threat groups, such as Storm-2949, have demonstrated how legitimate account recovery functionality can be manipulated to gain access to high-value executive and IT accounts. Once access is obtained, attackers move beyond traditional account compromise, targeting… Read more
Emerging Cyber Threat Trends Global SOC Teams Should Prepare For
Cybercriminals are leveraging new technologies, targeting new industries, and exposing operational weaknesses. The evolving threat landscape spans healthcare, finance, government, manufacturing, education, and critical infrastructure. No industry is safe from ransomware, supply chain compromise, cloud misconfiguration, social engineering, and nation-state activity. Global SOC teams need to look beyond detecting the latest threats. Building and scaling… Read more
Using AI Responsibly: Risks, Incidents, and Controls
Summary AI chatbots, including Claude, ChatGPT, or any other AI-powered chatbot, carry the inherent risk of unauthorized data exposure/loss. Since the introduction of AI chatbots to the public, multiple incidents have occurred that have either directly or indirectly resulted in unwanted data exposure. Non-exhaustive but impactful ways to reduce risk can be with AI usage… Read more
Why America is Cracking Down on Foreign Routers
Routers sit at the doorstep of our homes and small offices, they handle all traffic from Internet of Things (IoTs) to personal emails, family photos and even banking activity. Now, certain routers may be more difficult to obtain for anyone who is looking in the United States. The Federal Communications Commission (FCC) has announced on… Read more
Major Web Attacks: The Impact of the Shai-Hulud Worm
The Shai-Hulud Worm: What is it? How is it different? Shai-Hulud is a novel, self‑propagating software supply chain worm that targets the NPM (Node Package Manager) ecosystem and associated development, CI/CD, and cloud-connected environments. Historically, supply chain compromises required a human threat actor to breach a vendor, modify a product or update mechanism, and then… Read more