
Category: Security Operations Center
Supply Chain Attacks in 2026: When Trusted Software Turns Against You
From a major ad platform turned into a crypto-stealing network to open-source package repositories flooded with malicious code, supply chain attacks are exploiting trust at every level of the software stack. Read more
Zero-Click to Root: SonicWall VPN Gateways Under Active Ransomware Siege
INC Ransomware exploits SonicWall SMA flaws for zero-click root access while N-able and Wi-Fi gateways face parallel attacks—edge devices are the new frontline. Read more
AI Data Loss and Exposure: The New Threat Frontier
AI models are being hijacked to steal data, autonomous agents are breaking into servers, and employees feeding sensitive information into AI tools are creating a new category of data loss that traditional security tools were never designed to catch. Read more
Agentic Artificial Intelligence
When most people think of Artificial Intelligence (AI), they think of the widespread, commercial, chatbot-like platforms. You type something, and it types something back; the user initiates actions. An “agent” is different. It can browse the web, write and run code, call other software, and chain multiple steps together to complete a task without a… Read more
Why Firewalls and Edge Gateways are the New Primary Target
For a long time, the unwritten rule of initial access was simple- trick a human. Phishing and social engineering were the easiest ways into a network because people are notoriously easy to manipulate. While those vectors haven’t gone anywhere, the threat landscape has shifted drastically over the past year. Sophisticated threat actors are completely bypassing… Read more
Emerging Cyber Threat Trends Global SOC Teams Should Prepare For
Cybercriminals are leveraging new technologies, targeting new industries, and exposing operational weaknesses. The evolving threat landscape spans healthcare, finance, government, manufacturing, education, and critical infrastructure. No industry is safe from ransomware, supply chain compromise, cloud misconfiguration, social engineering, and nation-state activity. Global SOC teams need to look beyond detecting the latest threats. Building and scaling… Read more
Why America is Cracking Down on Foreign Routers
Routers sit at the doorstep of our homes and small offices, they handle all traffic from Internet of Things (IoTs) to personal emails, family photos and even banking activity. Now, certain routers may be more difficult to obtain for anyone who is looking in the United States. The Federal Communications Commission (FCC) has announced on… Read more
Your Devices May Be Spying on You — And You Would Never Know
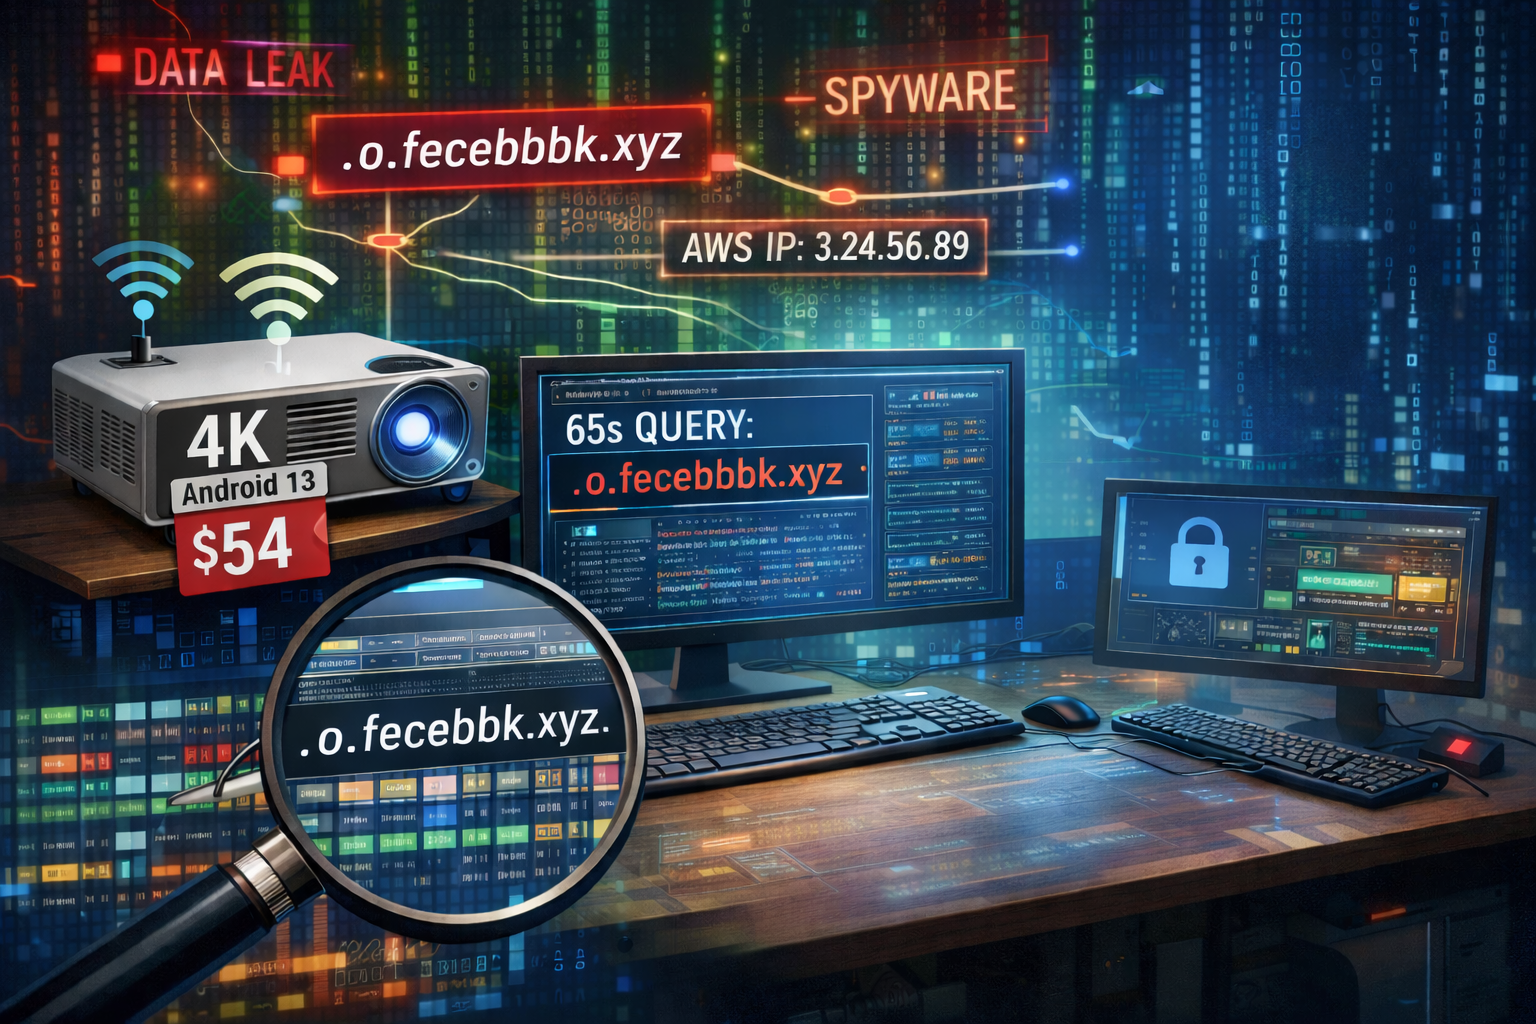
For anyone who frequently shops online, you may have noticed an increase in the number of electronic products sold by obscure, unheard of companies. Many of these products come with unbelievably, surprisingly affordable prices. A 4K projector with dual-band WiFi 6, 5G wireless, Bluetooth 5.2, and Android 13 for $54. What a deal. It almost… Read more
CTFs as a Training Tool for Blue-Space Operators
What is Capture the Flag (CTF)? If you do not already know or if you are new to cybersecurity, a CTF is essentially a simulated challenge where participants must solve puzzles or investigate clues to locate the “flag.” Most events use a jeopardy-style board with categories such as: Other formats use an attack-and-defend model where… Read more
Why SIEM is the Heartbeat of Security Operations
Did you know that every 11 seconds, a business becomes a victim of a cyberattack? Here’s a lesser-known fact. Signs of the attack could have been present for a long time, written in the firewall, server, or endpoint logs. The challenge is not the data. The question is, how quickly can an organization leverage that… Read more