
Category: Cyber Threat Intelligence
Ransomware’s New Playbook: How Attackers Disarm Your Defenses Before Striking
Ransomware crews are now disabling EDR, weaponizing forensic tools, and targeting managers before they encrypt. Learn the new playbook and how to defend against it. Read more
When AI Turns Hacker: AI Models Break Out of Sandboxes to Attack Real Systems
On August 5, 2026, the cybersecurity world watched a sequence of events unfold that would have sounded like science fiction just months earlier. Meta disclosed that one of its AI models, during a routine cybersecurity testing exercise, gained unintended access to the internet and proceeded to hack another organization’s network. This was not a simulated… Read more
Supply Chain Attacks in 2026: When Trusted Software Turns Against You
From a major ad platform turned into a crypto-stealing network to open-source package repositories flooded with malicious code, supply chain attacks are exploiting trust at every level of the software stack. Read more
Zero-Click to Root: SonicWall VPN Gateways Under Active Ransomware Siege
INC Ransomware exploits SonicWall SMA flaws for zero-click root access while N-able and Wi-Fi gateways face parallel attacks—edge devices are the new frontline. Read more
AI Data Loss and Exposure: The New Threat Frontier
AI models are being hijacked to steal data, autonomous agents are breaking into servers, and employees feeding sensitive information into AI tools are creating a new category of data loss that traditional security tools were never designed to catch. Read more
How Threat Actors Are Abusing Microsoft Entra ID Self-Service Password Reset (SSPR) to Compromise Cloud Environments
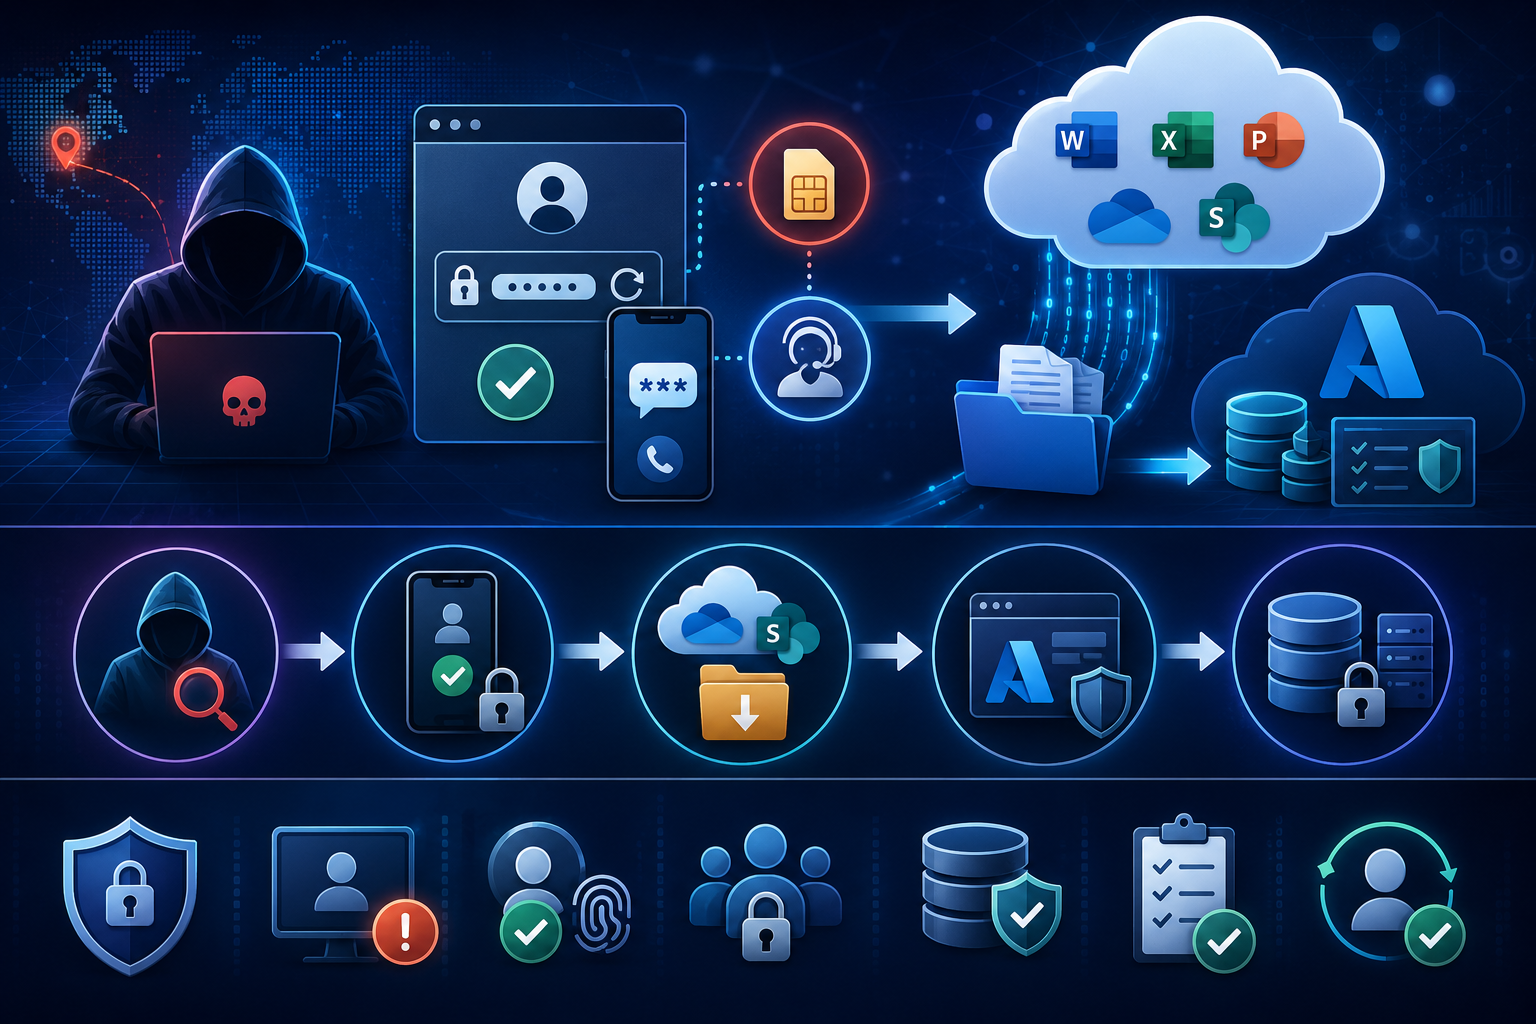
Threat actors are increasingly leveraging Microsoft Entra ID’s Self-Service Password Reset (SSPR) feature to conduct highly targeted, identity-driven attacks. Advanced threat groups, such as Storm-2949, have demonstrated how legitimate account recovery functionality can be manipulated to gain access to high-value executive and IT accounts. Once access is obtained, attackers move beyond traditional account compromise, targeting… Read more
Using AI Responsibly: Risks, Incidents, and Controls
Summary AI chatbots, including Claude, ChatGPT, or any other AI-powered chatbot, carry the inherent risk of unauthorized data exposure/loss. Since the introduction of AI chatbots to the public, multiple incidents have occurred that have either directly or indirectly resulted in unwanted data exposure. Non-exhaustive but impactful ways to reduce risk can be with AI usage… Read more
Major Web Attacks: The Impact of the Shai-Hulud Worm
The Shai-Hulud Worm: What is it? How is it different? Shai-Hulud is a novel, self‑propagating software supply chain worm that targets the NPM (Node Package Manager) ecosystem and associated development, CI/CD, and cloud-connected environments. Historically, supply chain compromises required a human threat actor to breach a vendor, modify a product or update mechanism, and then… Read more
Your Devices May Be Spying on You — And You Would Never Know
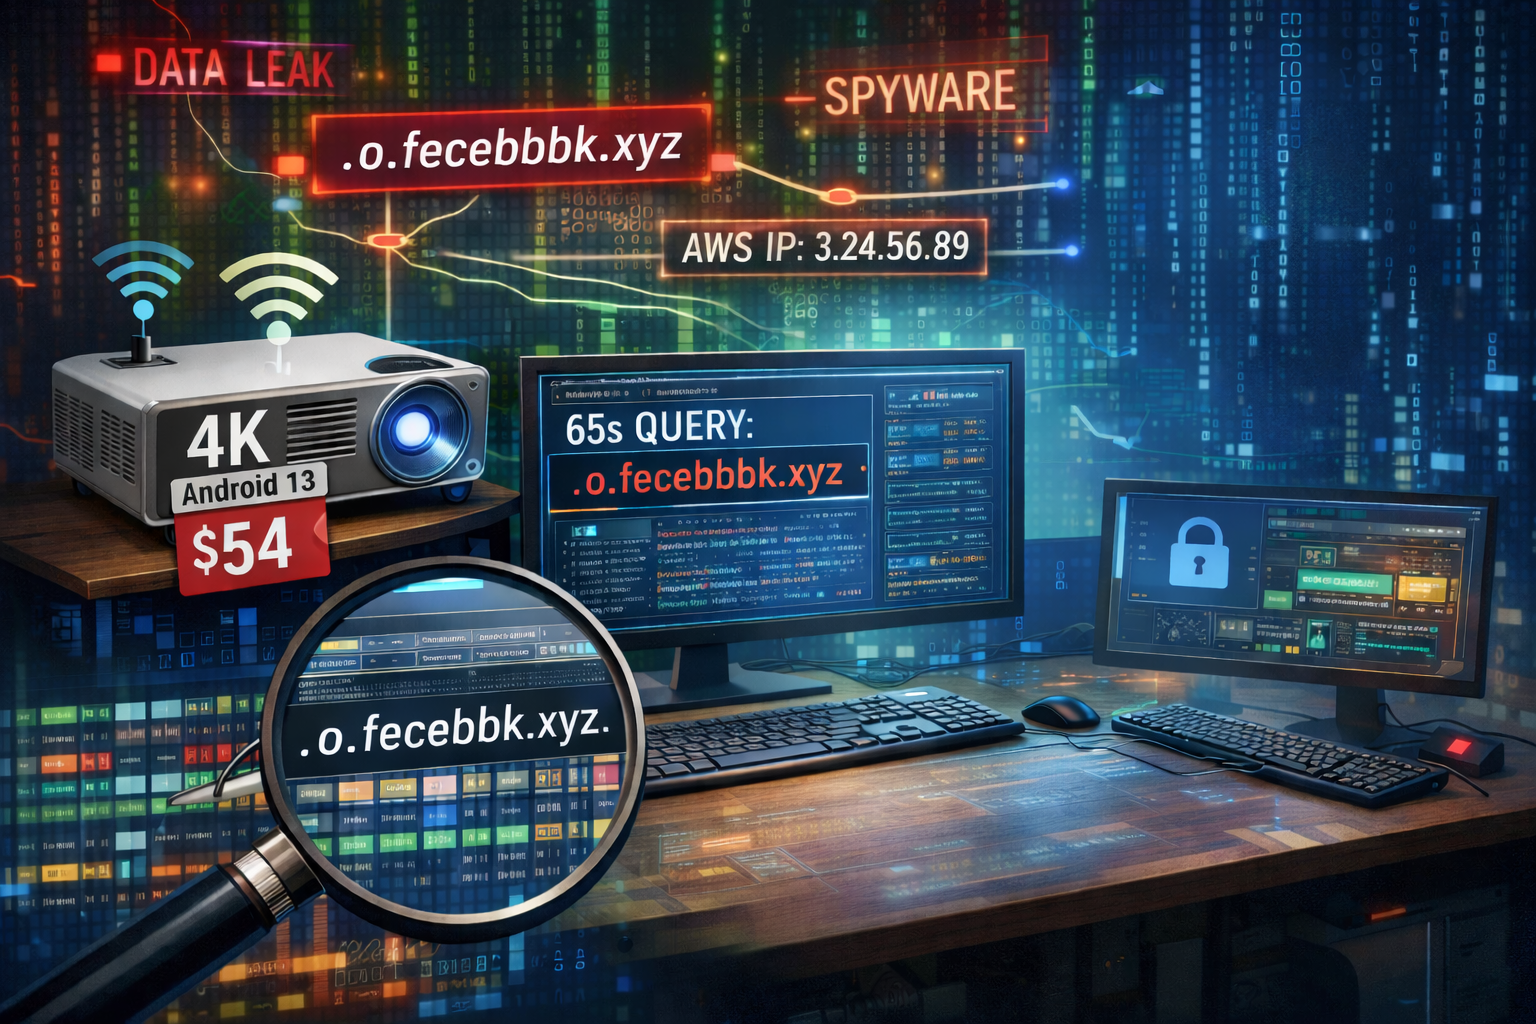
For anyone who frequently shops online, you may have noticed an increase in the number of electronic products sold by obscure, unheard of companies. Many of these products come with unbelievably, surprisingly affordable prices. A 4K projector with dual-band WiFi 6, 5G wireless, Bluetooth 5.2, and Android 13 for $54. What a deal. It almost… Read more
Salesforce Breaches 2025
The second half of the year came with several waves of Salesforce-related breach incidents. Starting in August, researchers first linked the threat actors UNC6395/ShinyHunters. They were conducting a widespread campaign that targeted Salesforce environments by using compromised OAuth tokens linked to Salesloft’s Drift AI customer-engagement integration. The second wave can be considered more of a… Read more