
DefendEdge Cyber Security Blog
CISA Urges Hardening Fortinet Devices After Reports of Credential Exposure
CISA is aware of global reports that malicious cyber actors have targeted internet-accessible Fortinet devices across government and private sector organizations using compromised credentials. This activity, referred to as FortiBleed, involves the exposure of leaked credentials associated with approximately 74,000 Fortinet devices, including firewalls and virtual private network (VPN) gateways. To defend against this…
Vulnerability Summary for the Week of June 8, 2026
High Vulnerabilities PrimaryVendor — Product Description Published CVSS Score Source Info AdguardTeam–AdGuardHome AdGuard Home, when started with the –glinet flag, contains an authentication bypass vulnerability that allows unauthenticated attackers to gain full admin access by supplying a path traversal sequence in the Admin-Token cookie, exploiting unsanitized string concatenation in the token file path construction within…
Vulnerability Summary for the Week of June 1, 2026
High Vulnerabilities PrimaryVendor — Product Description Published CVSS Score Source Info 10Web–Photo Gallery by 10Web Improper Neutralization of Special Elements used in an SQL Command (‘SQL Injection’) vulnerability in 10Web Photo Gallery by 10Web allows Blind SQL Injection. This issue affects Photo Gallery by 10Web: from n/a through 1.8.41. 2026-06-04 7.6 CVE-2026-49771 AAM Plugin–Advanced Access…
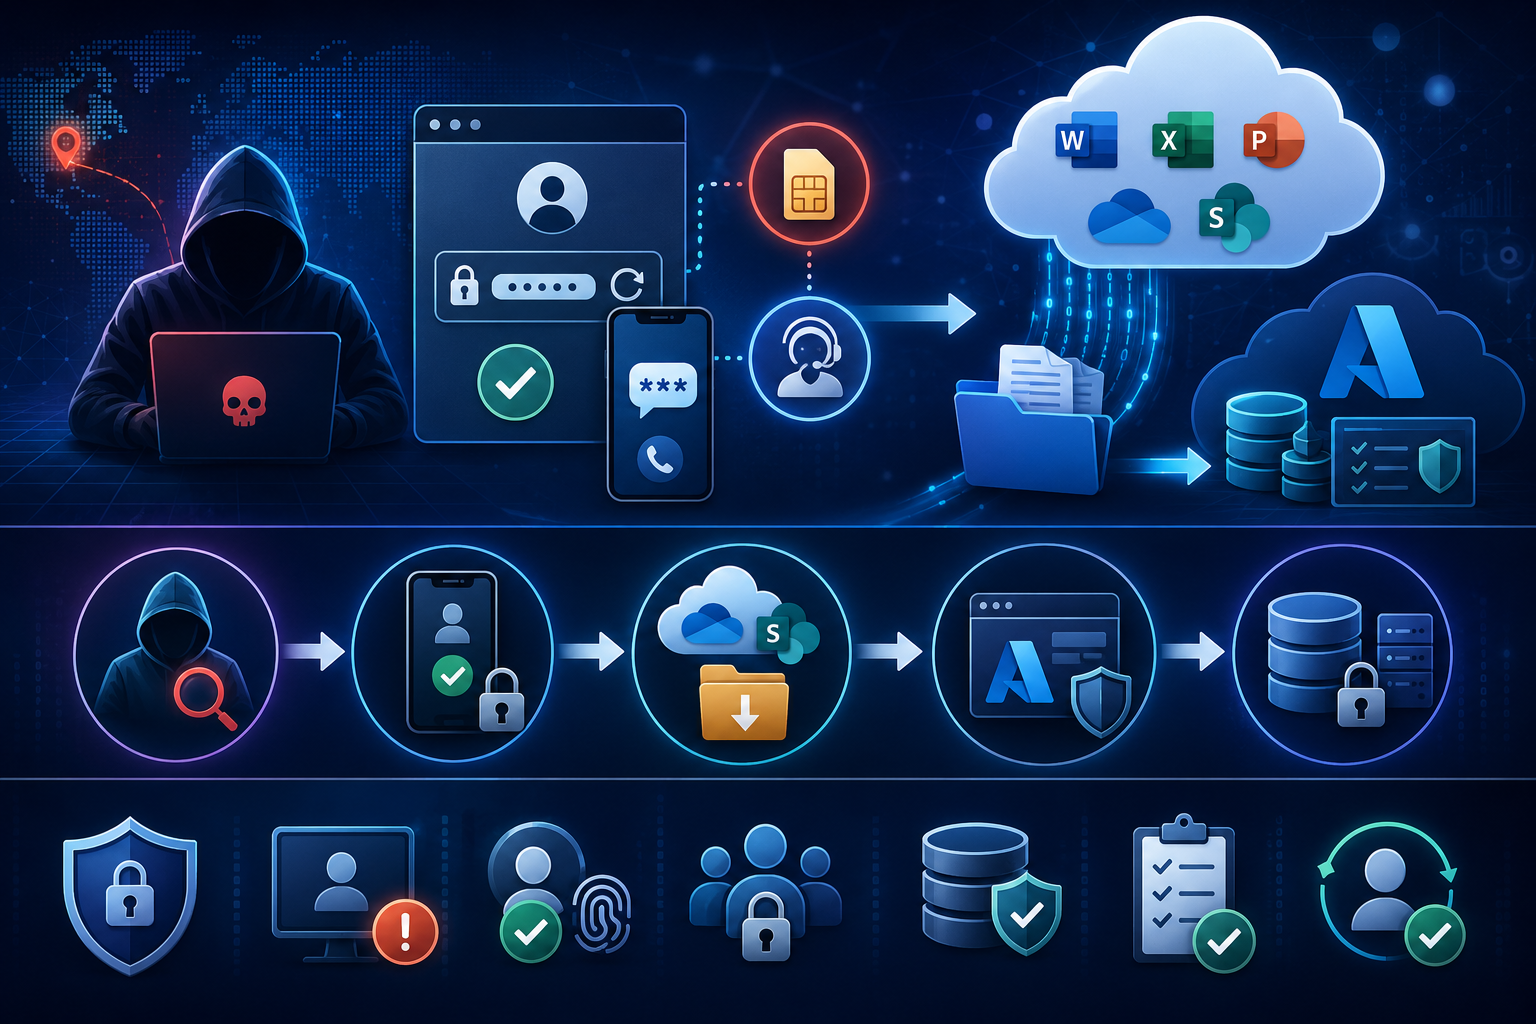
How Threat Actors Are Abusing Microsoft Entra ID Self-Service Password Reset (SSPR) to Compromise Cloud Environments
Threat actors are increasingly leveraging Microsoft Entra ID’s Self-Service Password Reset (SSPR) feature to conduct highly targeted, identity-driven attacks. Advanced threat groups, such as Storm-2949, have demonstrated how legitimate account recovery functionality can be manipulated to gain access to high-value executive and IT accounts. Once access is obtained, attackers move beyond traditional account compromise, targeting…
Vulnerability Summary for the Week of May 25, 2026
High Vulnerabilities PrimaryVendor — Product Description Published CVSS Score Source Info 1Panel-dev–MaxKB MaxKB is an open-source AI assistant for enterprise. Prior to 2.9.0, MaxKB’s webhook trigger endpoint (/api/trigger/v1/webhook/{trigger_id}) is accessible without authentication. The WebhookAuth class unconditionally returns (None, {}), which Django REST Framework interprets as successful authentication. Combined with optional per-trigger token verification and no…
Supply Chain Compromises Impact Nx Console and GitHub Repositories
CISA is prioritizing the response to multiple emerging software supply chain intrusion campaigns targeting developer ecosystems Continuous Integration/Continuous Development (CI/CD) pipelines. These recent incidents, including the GitHub compromise via a malicious Nx Console Visual Studio Code (VS Code) extension and the “Megalodon” supply chain intrusion campaign, demonstrate how cyber threat actors are abusing tools and…
Vulnerability Summary for the Week of May 18, 2026
High Vulnerabilities PrimaryVendor — Product Description Published CVSS Score Source Info 10-Strike–Network Inventory Explorer 10-Strike Network Inventory Explorer 8.54 contains a stack-based buffer overflow vulnerability in the registration key input field that allows local attackers to execute arbitrary code by triggering a structured exception handler overwrite. Attackers can craft a malicious registration key string with…
Emerging Cyber Threat Trends Global SOC Teams Should Prepare For
Cybercriminals are leveraging new technologies, targeting new industries, and exposing operational weaknesses. The evolving threat landscape spans healthcare, finance, government, manufacturing, education, and critical infrastructure. No industry is safe from ransomware, supply chain compromise, cloud misconfiguration, social engineering, and nation-state activity. Global SOC teams need to look beyond detecting the latest threats. Building and scaling…
Vulnerability Summary for the Week of May 11, 2026
High Vulnerabilities PrimaryVendor — Product Description Published CVSS Score Source Info Patch Info acl–ACL Analytics ACL Analytics versions 11.x through 13.0.0.579 contain an arbitrary code execution vulnerability that allows attackers to execute arbitrary commands by leveraging the EXECUTE function. Attackers can use bitsadmin to download malicious PowerShell scripts and execute them with system privileges to…
Vulnerability Summary for the Week of May 4, 2026
High Vulnerabilities PrimaryVendor — Product Description Published CVSS Score Source Info Patch Info gotenberg–gotenberg Gotenberg is a Docker-powered stateless API for PDF files. In versions 8.30.1 and earlier, the metadata write endpoint validates metadata keys for control characters but leaves metadata values unsanitized. A newline character in a metadata value splits the ExifTool stdin line…